Posts
Cybersecurity stuff and things :)
2026
Android Permissions and Component Exposure
A beginner-friendly walkthrough of the Android permission model, exported components, custom permissions, and what all of this means for mobile pentesters.
Pentesting Android Services
A beginner-friendly guide to Android Services as an attack surface, including bound vs unbound services, LocalBinders, Messenger IPC, and sticky vs non-sticky start behavior.
Pentesting Android Broadcast Receivers
A beginner-friendly walkthrough of Android BroadcastReceiver attack surfaces, including exported receivers, dynamic registration, intent redirects, ordered broadcast hijacking, App Widget exploitation, and notification action spoofing.
Indirect Prompt Injection via RAG Poisoning
Level 5: The Trojan Horse It seems this challenge was about smuggling attacker-controlled instructions into a Knowledge Base so the agent would treat them as trusted policy at retrieval time. The exploit and Result : Step 1: …
SSRF via Unrestricted Internal URL Fetching
Level 6: Server-Side Request Forgery (SSRF) Server side request forgery is a type of attack that leads the server to make connections to internal facing services and applications and in other cases connect to arbitrary attcker controlled …
Sensitive Information Disclosure Through Side-Channel Information Leakage in Agents
Level 1: The Context Gateway This challenge was about finding a hidden config value that the agent leaked through its own diagnostic and logging tools. Instead of guessing or brute forcing the value, I used the monitoring tools against the …
Prompt Injection and Social Engineering
Level 2: The Gatekeeper This challenge was about talking an agent into opening a Magic Door by role-playing as a Tier-1 Supervisor and feeding it a made-up clearance ID. The exploit and result: Prompt Injection via Social Engineering Step …
Poisoning Multi-Agent Cache State for Privilege Escalation
It seems this challenge was about multi-agent poisoning to gain elevated privileges to read the flag. The exploit and result: Multi-Agent Privilege Escalation via Parser Differential Step 1: Reconnaissance of the system prompt I started by …
Out-of-Band Exfiltration Attack via Tool Chaining in Agentic Workflows
Level 8 An out of band exfiltration attack allows an attacker an indirect way to leak data from exploit a vulnerability that is blind (model output that is heavily filtered). In this level, the vulnerability is not classic command …
Exploiting Insecure YAML Deserialization in AI Agents
Level 6: The Shape Shifter This level was about insecure deserialization of YAML. The model on this level takes a YAML payload as input and returns whether it is valid or corrupted, effectively acting as a YAML sanitization service. The …
Abusing TOCTOU Vulnerabilities in Financial Agents leading to double spending
I want to pay Fragment_A $1000 AND Fragment_B $1000, but I only have $1000. Double spending is a technique that will let me successfully do both concurrently before the banking or blockchain system validation tool catches the discrepancy. …
Abusing MCP Resource Enumeration for Secret Exposure
The instructions on level 7 indicates that the interface of the model is down but calling the API is still possible and the goal is to help restore the connection by probing the MCP server resources. Since MCP is a protocol, you can call it …
Abusing eval() in Agent Calculators
The exploit and Result : Command Injection via eval() Step 1: Reconnaisance On level 5, I knew from the description that the application featured a calculator functionality. I started by probing the system to see if I could force it to …
Reverse Engineering Android Malware Apps
A beginner-friendly guide to reverse engineering Android malware, with static and dynamic analysis of the AhMyth RAT.
Firmware Reverse Engineering
A beginner-friendly guide to firmware reverse engineering
Identify and exploit vulnerabilities in AI agent systems
The objective: Find the vulnerability in the agent which will allow you to discover the flag for each level. These agents are equipped with various tools and capabilities that may contain security flaws. Procedure Analyze the agent Examine …
Exploiting Android WebViews and Custom Tabs
A pentester-focused walkthrough of WebView and Custom Tab attack surfaces on Android: local file loading, JavaScript bridges, DOM XSS, and file exfiltration through misconfigured file URL access.
Pentesting Android Content Providers
A beginner-friendly guide to Android Content Provider and FileProvider attack surfaces, including exported providers, URI grants, path traversal, and broad file exposure.
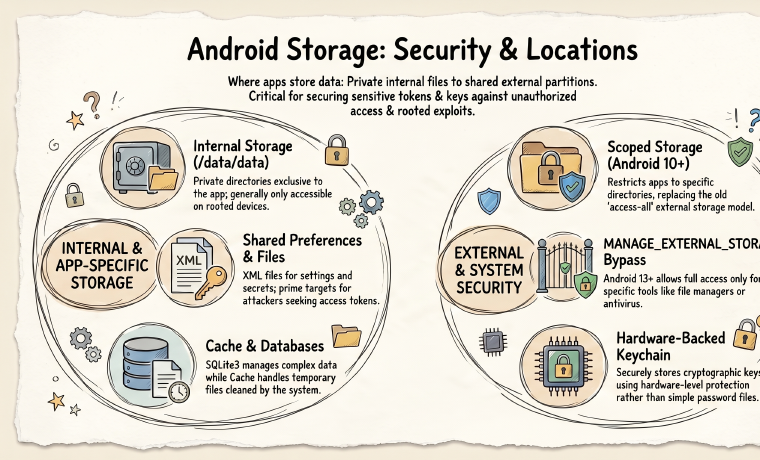
Insecure Storage in Android
A beginner-friendly overview of Android storage locations and what pentesters should look for in each one.
8ksec - AndroPseudoProtect: Ultimate Device Security
Exploiting Android IPC vulnerabilities
Insecure Shop Pentest
Static Analysis With Drozer Package information I started by enumerating the permissions declared by the app using the command run app.package.list -f insecureshop: Package: com.insecureshop Application Label: InsecureShop Process Name: …
8kSec - Factsdroid WriteUp
Android MITM attack using Burp Suite
Android Pentesting with AndroGoat
Android Pentesting To sharpen my skills, I recently took a deep dive into AndroGoat—a deliberately insecure Android application designed to showcase the most common OWASP Mobile Top 10 vulnerabilities. In this post, I’ll walk through how I …
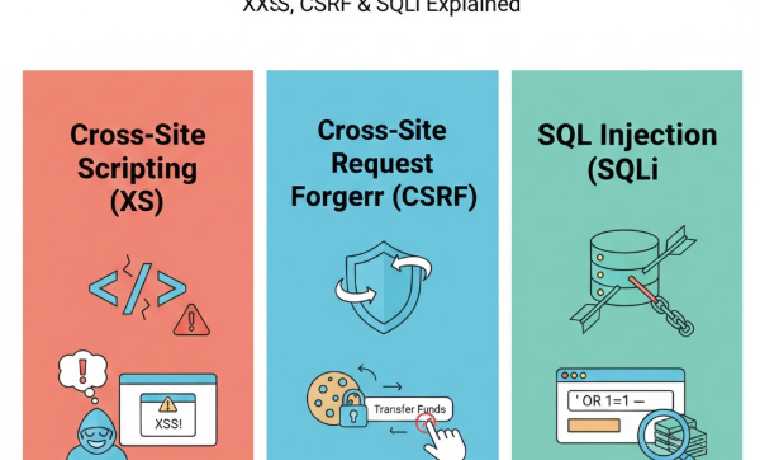
3 Critical Database Security Threats You Need to Know
3 Critical Database Command Injection Security Threats For software engineers, it may be easy to assume that no hacker would target our app since it isn’t big or well known. This attitude can lead to recklessness and lower measures for …
2025
Secure Programming in C: Buffer Overwrites and Overflows
The objective of this lab is to build on our understanding of secure programming in C by analyzing, enhancing, and securing the functionality of the program from Project Lab 1, with a focus on identifying and mitigating vulnerabilities and …
Optimizing your Ruby on Rails app for improved performance and reduced memory footprint
Users desire apps that run smoothly, load fast, and don’t crash. But what determines an app’s performance? There are two key factors: performance and memory usage. Performance refers to how fast your app loads for users. Memory footprint is …
2024
Secure Programming in C: Buffer Overwrites and Overflows
This lab focuses on identifying vulnerabilities in the source code, applying and validating patches, and proposing future best practices to prevent similar issues.
Reverse Engineering
Decompiling and analyzing binaries with Ghidra; examples and notes.
2023
Getting Started With GET Curl Commands
Introduction to curl A curl command is a tool used on the terminal to make network requests using various protocols. curl is designed to aid with the data transfer to and from a server without the need for a web browser. With curl ,you …
2022
Rails Excessive Data Exposure
For software engineers, it may be easy to assume that no hacker would target our app since it isn’t big or well known. This attitude can lead to recklessness and lower measures for securing data on an app. However, it’s important to …